UNICESS · BLOCKCHAIN STUDENT IDENTITY
Institutional identity,
on-chain. Performed live.
UNICESS is a blockchain-backed student identity system for Android. A live demo needs two phones, a funded testnet, and network availability — so this site performs it instead: scripted, scroll-driven Demo Runs inside a Mock Phone.
SIMULATED WALKTHROUGH · NO BLOCKCHAIN · NO BACKEND · NO LIVE DATAFLAGSHIP · QR CREDENTIAL FLOW
Two phones. One verification.
UNICESS's QR verification needs a student, a verifier, and the blockchain — two or more phones in real life. Here both devices sit side by side, and the Demo Run performs the whole exchange in one scroll.
Generating QR credential... Please confirm the key generation request.
Two phones. One verification.
FACULTY: FICT
PHONE: +60 12-345 6789
Never Verified Before
KEEP SCROLLING — THE DEMO PLAYS WITH YOUR SCROLL
ADMIN CONSOLE · ROLE-SWITCH
Every management move, on-chain.
The same phone, switched to the Registrar Office's Admin role: search the registry, edit an account, delete it — then the audit trail, where every action is recorded. Above the Admin sits the contract Owner, the role that grants every Admin their power.
One phone, a new role: the Registrar Office's Admin console.
KEEP SCROLLING — THE DEMO PLAYS WITH YOUR SCROLL
VERIFY & SEARCH
Verify any presented credential and search the on-chain identity registry — the console's daily work.
AUDIT TRAIL
Every verification, edit, and deletion is recorded on-chain and readable in the console — Success, Reverted, Pending.
EDIT
Deactivate or activate an account with one signed action — the edit the audit records as Changed Account Status.
DELETE
Delete a student identity on-chain when the Registrar Office says so — the contract demands a second confirmation.
OWNER
The contract owner's view: assign or revoke Admin roles and read the contract owner name.
PUBLIC LEDGER · WHAT THE PUBLIC SEES
Public on-chain. Readable in the app.
Every action lives on a public blockchain — anyone can audit it. But a raw block explorer is complicated and confusing for non-technical people. The app turns those rows into simple, readable events, with full information about the action that happened within the smart contract.
| Status | Txn Hash | Method | Block | Age | From | To | Amount |
|---|---|---|---|---|---|---|---|
| ✓ | 0x8f3a…3f5a | Deleted Account | 5958551 | 3 mins ago | 0x3E9a…4a91 | 0x5C77…21B1 | 0 ETH |
| ✓ | 0x4a7c…7a5f | Changed Account Status | 5958535 | 6 mins ago | 0x3E9a…4a91 | 0x5C77…21B1 | 0 ETH |
| ✓ | 0x6c8e…8c3e | Record Verification | 5957506 | 3 hrs 32 mins ago | 0x3E9a…4a91 | 0x5C77…21B1 | 0 ETH |
| ✕ | 0x9e7d…2a0c | Record Verification | 5957498 | 3 hrs 33 mins ago | 0x3E9a…4a91 | 0x5C77…21B1 | 0 ETH |
| ✓ | 0x1e3d…2a0c | Assigned Admin Role | 5655106 | 42 days ago | 0x5F2c…2e84 | 0x5C77…21B1 | 0 ETH |
| ✓ | 0x3b5d…6b8d | Account Registered | 5547106 | 57 days ago | 0x842b…23b5 | 0x5C77…21B1 | 0 ETH |
INPUT DATA | |||||||
AI CHAT · UTAR AI ASSISTANT
An assistant built into the app.
UNICESS ships with the UTAR AI Assistant — chat support that answers questions about the system without leaving the app. A server runs a scheduled Python scraper that ingests the UTAR website into a ChromaDB RAG index, and a local ministral-3:3b model answers from it, so the assistant handles UTAR questions (like intake dates) a general AI model can't.
The UTAR AI Assistant, one tap away in the app.
READY — ASK ME ANYTHING
KEEP SCROLLING — THE DEMO PLAYS WITH YOUR SCROLL
SECURITY
Hardware-backed. On-chain. Private.
Two keys carry the whole trust model: a hardware-bound biometric key that signs inside the phone's secure hardware, and a runtime-generated delegate key that signs on-chain. The Demo Run below performs both key ceremonies.
0x842b…23b5|1735689600|0x3045…e6d9UNICESS represents the next generation of institutional identity management, built entirely on the Ethereum Blockchain. By leveraging Hardware-Backed Biometric Cryptography (secp256r1) and on-chain Smart Contracts, this system completely eliminates the possibility of ID forgery, screenshot replays, and unauthorized cloning. All sensitive Personal Information (PII) is secured using AES-GCM encryption, ensuring that only authorized University personnel hold the decryption rights, maintaining strict user privacy while benefiting from the transparency of Web3.
0x842b3F1c5e0dA7f13b8d5eC3bA4e0f7aC2Ea23b5Two keys guard one identity.
KEEP SCROLLING — THE DEMO PLAYS WITH YOUR SCROLL
HARDWARE KEYSTORE
The signing key is an Android Keystore pair — secp256r1 with SHA-256, purpose SIGN, user authentication required, invalidated by new biometric enrollment. Its private half never leaves secure hardware; the app holds only the public key.
RUNTIME DELEGATE KEYS
A separate secp256k1 key is generated at runtime and persisted only in AES-256-GCM EncryptedSharedPreferences. It signs the wallet's MetaMask transactions and is bound to the identity on-chain — linkDelegate() fires the DelegateLinked event.
ENCRYPTED PII
All personal information is AES-GCM encrypted before it touches the chain — only authorized university personnel hold decryption rights.
RESEARCH
From FYP to product.
UNICESS began as a UTAR Final Year Project — the poster is the project's research summary, and the thesis lives in the university's institutional repository.
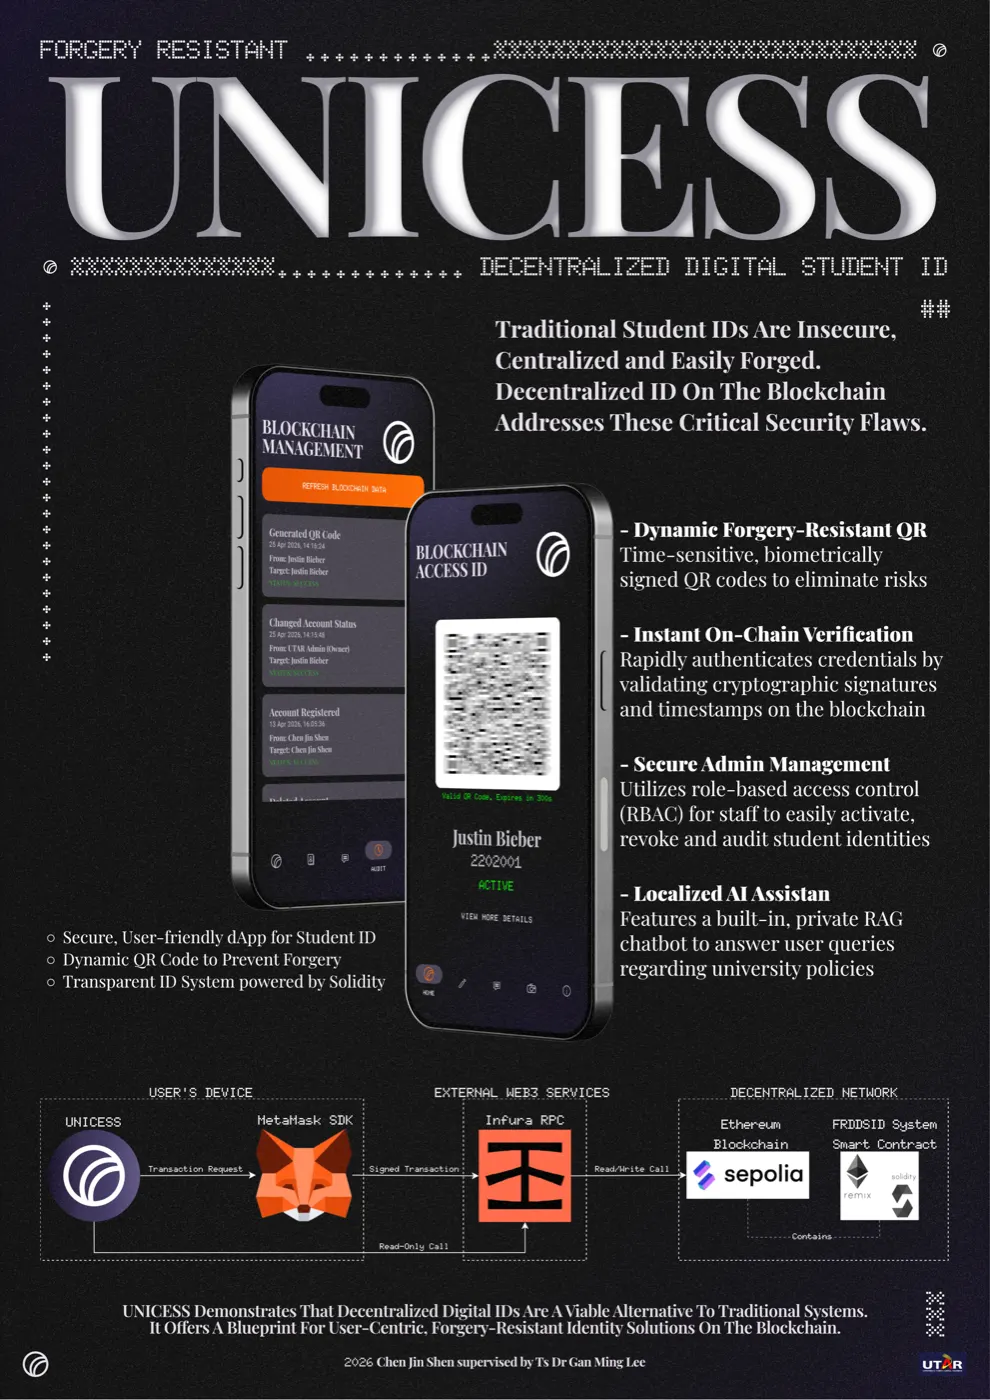
Selected for the UTAR Institutional Repository
Chen, Jin Shen (2026) Forgery resistant decentralized digital student ID. Final Year Project, UTAR.
Repository record ↗